Memory-safe Rust
The Rust component of the PQSecure-SW™ stack. A production-grade, memory-safe implementation of the NIST post-quantum standards for systems where memory safety and side-channel resistance are not negotiable.
Parameter sets
| Module | Standard | Level |
|---|---|---|
| ML-KEM-512 | FIPS 203 | 1 |
| ML-KEM-768 | FIPS 203 | 3 |
| ML-KEM-1024 | FIPS 203 | 5 |
| ML-DSA-44 | FIPS 204 | 2 |
| ML-DSA-65 | FIPS 204 | 3 |
| ML-DSA-87 | FIPS 204 | 5 |
Algorithm coverage
The finalized NIST post-quantum standards at every parameter set, with the hash primitives hybrid deployments still depend on.
Complete software portfolio
NIST post-quantum
- ML-KEM FIPS 203
- ML-DSA FIPS 204
- SLH-DSA (SPHINCS+) FIPS 205
- FN-DSA (Falcon) FIPS 206, available soon
Stateful signatures
- XMSS RFC 8391
- LMS RFC 8554
- Stateful guidance NIST SP 800-208
Hash and classical
- SHA-2 FIPS 180
- SHA-3 (Keccak) FIPS 202
- SHA-2, HMAC, HKDF RFC 6234
TRUST is the memory-safe Rust implementation within the PQSecure-SW portfolio. It supports the relevant NIST security levels, 1, 3, and 5 where applicable.
Proven for every input, not just the tested ones
Kani is the Rust verification tool developed by AWS. It runs CBMC as its backend engine and proves correctness properties for every possible input within defined bounds, rather than only the inputs covered by tests.
Two routes, one engine
libpqsecure-C is verified with CBMC directly. libpqsecure-rs reaches the same solver through Kani. Both halves of the stack answer to one proof engine.
See the full stack →What Kani proves
-
Panic freedom
No
unwrap, index bounds, or division by zero, on any code path - Arithmetic overflow No integer operation can overflow
-
Memory safety in unsafe blocks
The few
unsafeboundaries are proven, not reviewed - Cryptographic invariants Custom assertions checked for every parameter set
- Constant-time execution Execution independent of secret key material
One implementation, desktop to bare metal
no_std support means the verified implementation that runs on a workstation is the same one that runs on a microcontroller.
-
Target class
Desktop and server
Full standard library
- Linux
- x86-64
- macOS
- ARM and x86
- Windows
- Supported
-
Target class
Embedded and MCU
Bare-metal, no standard library
- RISC-V
- RV32 and RV64
- ARM
- Cortex-M
- Bare-metal
no_std
Pairs with libpqsecure-asm for architecture-specific NTT and polynomial arithmetic acceleration on ARM Cortex-M4 and M33 and on RISC-V targets.
Where it goes
Built for systems where memory safety and provable correctness are requirements rather than preferences.
Engineered for
- Memory-safe cryptographic implementation
- Formally proven correctness
- Embedded and bare-metal deployment
- NIST-standardized algorithm compliance
- Strong type enforcement at the API boundary
We combine
- Kani formal verification
- Rust ownership
- Constant-time, side-channel-aware implementation
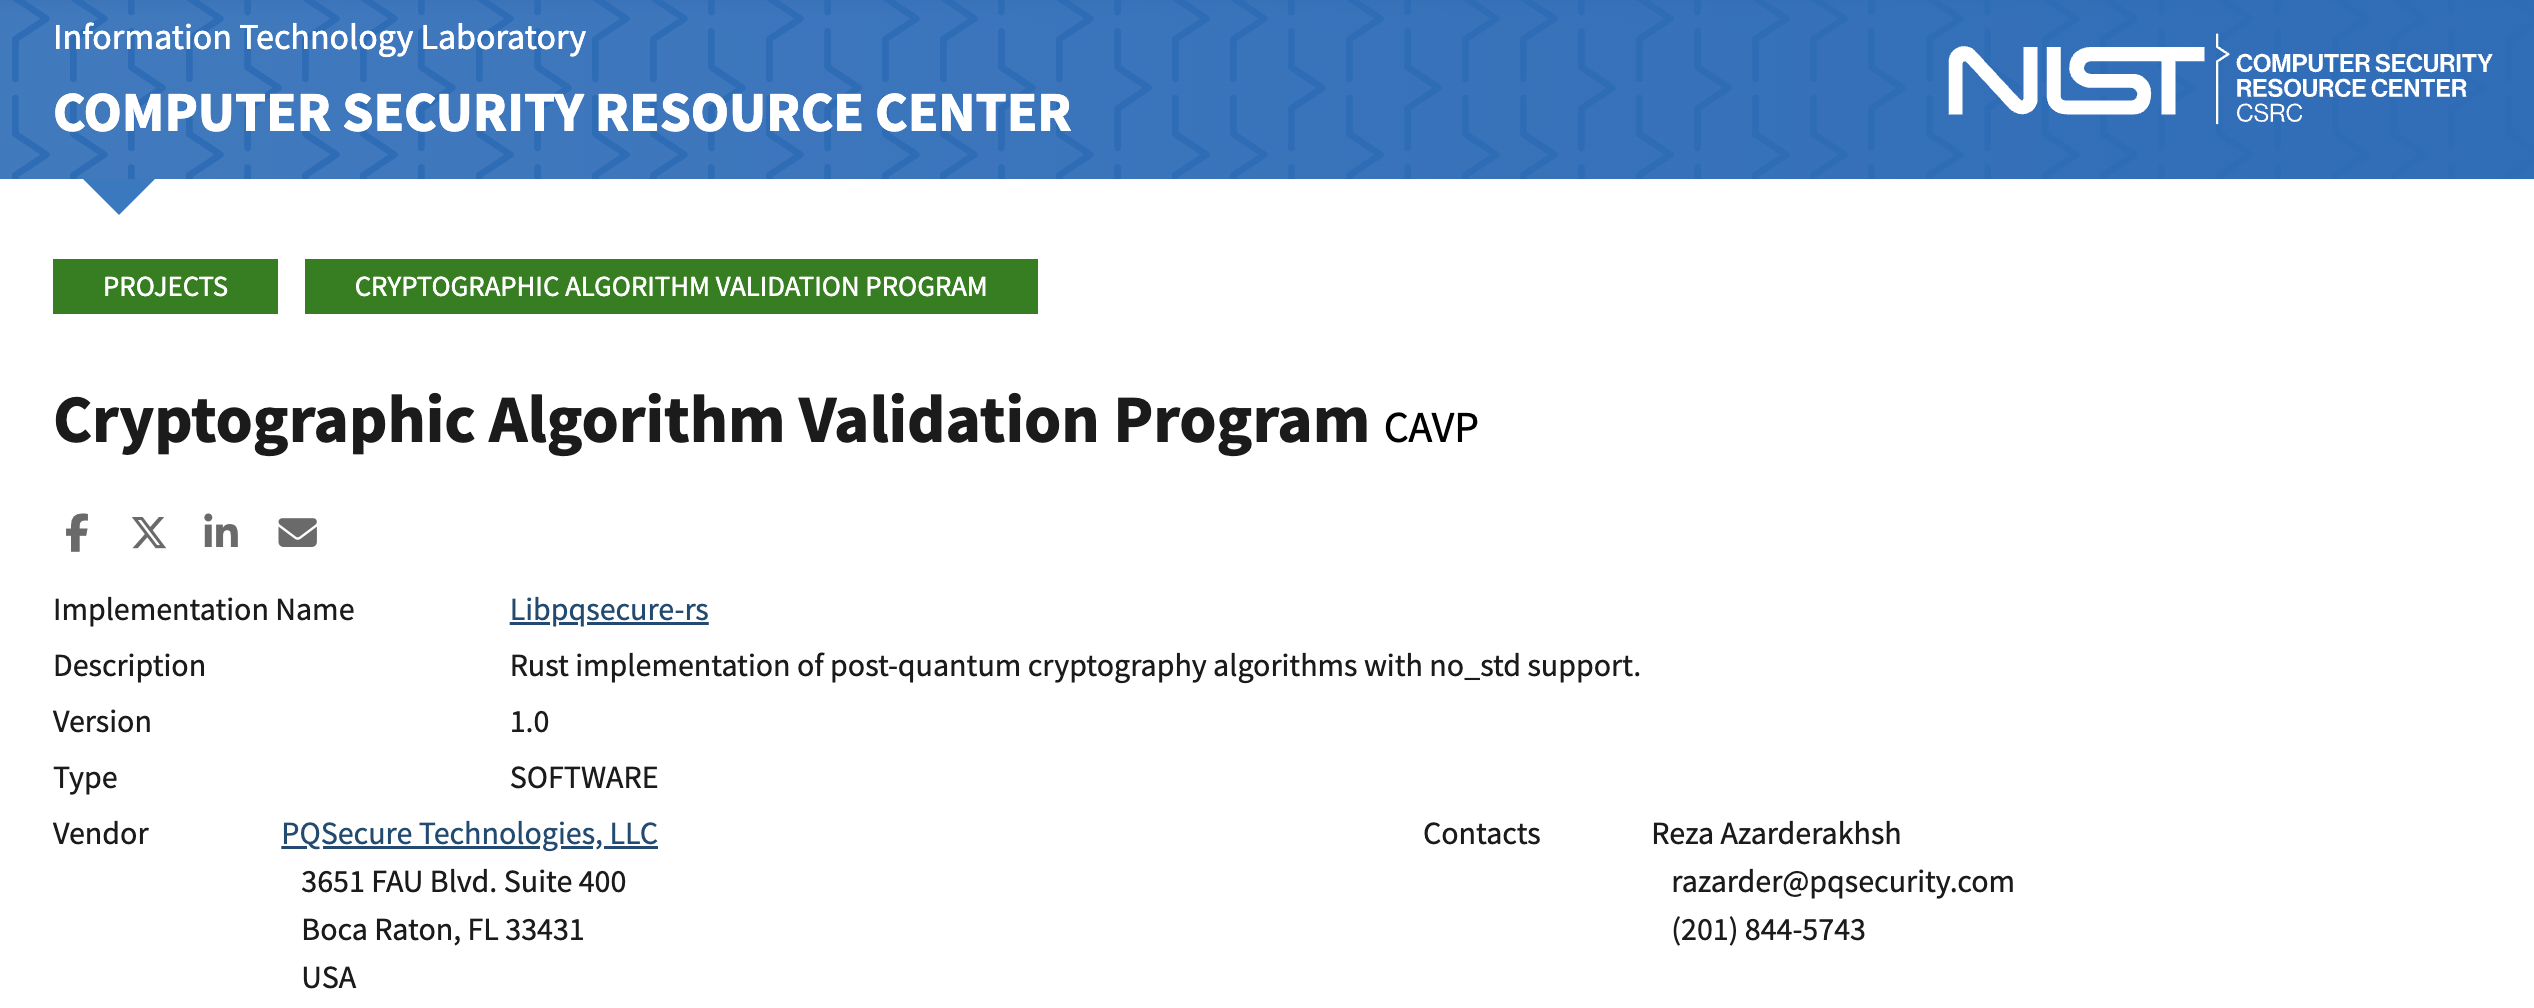
- ACVP-tested and CAVP certified
- Drop-in complement to libpqsecure-C
to deliver production-ready, high-assurance quantum-safe cryptography.
View the full software stack →Certification
 A7616
Cryptographic Algorithm Validation Program
Rust implementation of post-quantum cryptography algorithms with no_std support.
- Validated
-
- ML-KEM FIPS 203
- ML-DSA FIPS 204
- Vendor
- PQSecure Technologies
The C implementation is certified separately under A6936. See PQSecure-SW →
Memory-safe cryptography for mission-critical systems.
Talk with our team about integration, licensing, and embedded deployment.
Contact us